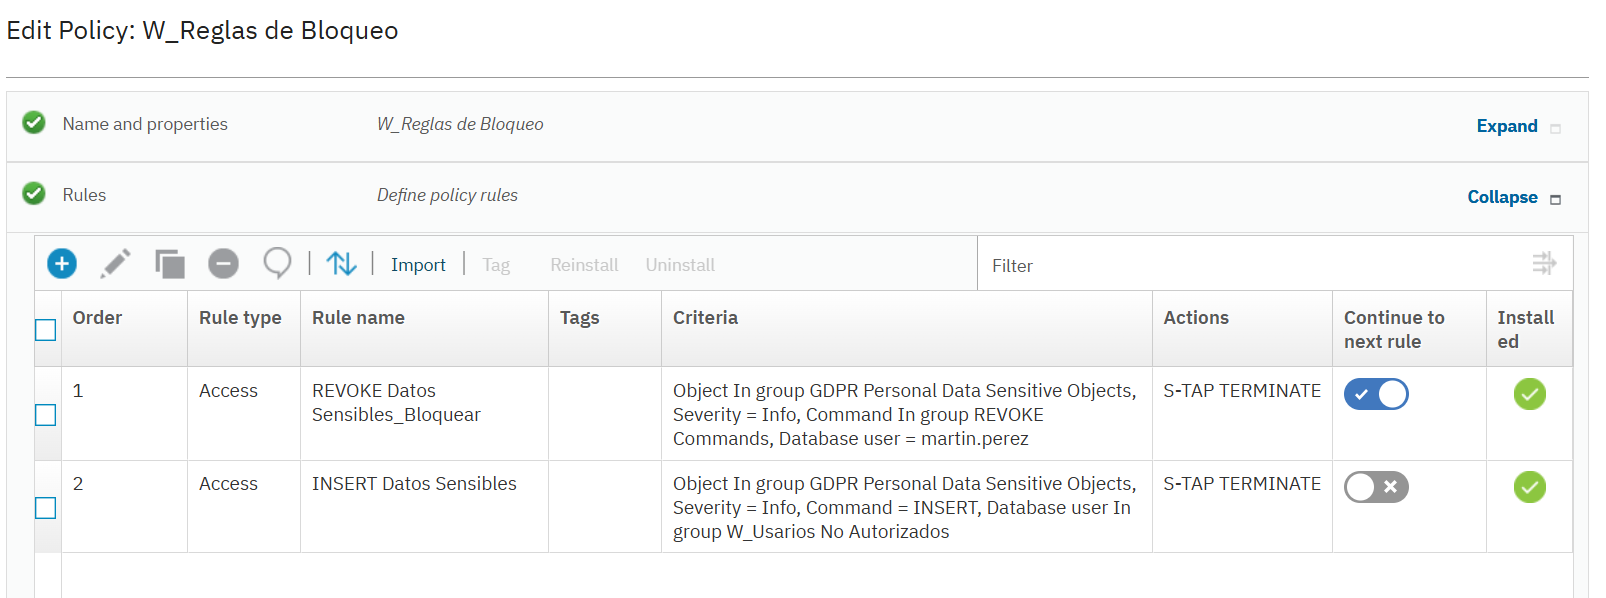
I have two blocking rules in Guardium. In this case, I am using a MySQL database, and the firewall is set to "close mode."
Fist Rule:
Database user = martin.perez
Object In group GDPR Personal Data Sensitive Objects
Command In group REVOKE Commands
Action: S-TAP TERMINATE
Second Rule:
Database user In group W_Usarios No Autorizados
Object In group GDPR Personal Data Sensitive Objects
Command = INSERT
Action: S-TAP TERMINATE
When the user `martin.perez` executes a `REVOKE` command, the session becomes blocked; however, when a user executes an `INSERT`, the session allows the SQL statement.
I have tried configuring these rules in different ways, but the result is not what I expected.
Does anyone know how these blocking rules work?
How should I configure the rules or policies?