This blog discusses the nuances when making IBM Storage Defender Copy Data management (CDM) work with its MS SQL Agent installed on Windows Server configured with Microsoft Windows Defender.
- Microsoft Defender Antivirus is a built-in security program by Microsoft that protects Windows from viruses and malware.
- Microsoft Defender for Endpoint is an enterprise endpoint-security platform that includes broader protection, detection, investigation, response, and centralized management capabilities.
- IBM Defender Copy Data Management is enterprise software for controlling, automating, and reusing copies of data.
Root Cause Summary
Microsoft Defender Antivirus flags CDM agent components because they:
- Inject into the VSS/VDI subsystem at a low level (similar to rootkit-like behaviour from Defender's heuristic engine)
- Create transient named pipes and COM objects for VDI coordination
- Establish WinRM sessions originating from a non-domain or external IP (the CDM appliance)
- Write/read large binary streams rapidly to/from SQL VSS shadow copies
Remediation
1. Process Exclusions — ecxagent.exe and sqlvdiwrapper.exe
Add these as Process exclusions (not just path exclusions) in Microsoft Defender Antivirus. Process exclusions suppress scanning of all file I/O initiated by the process.
Via PowerShell (run as Administrator on each SQL Server host):
# CDM Agent process exclusions
Add-MpPreference -ExclusionProcess "ecxagent.exe"
Add-MpPreference -ExclusionProcess "sqlvdiwrapper.exe"
Add-MpPreference -ExclusionProcess “ecxvssreq.exe”
# Also exclude the full paths if the binaries are in a fixed location (adjust path as needed)
Add-MpPreference -ExclusionPath "C:\Program Files\IBM\IBM Storage Defender Copy Data Management"
Add-MpPreference -ExclusionPath "C:\Program Files\Catalogic Software\ECX"
# Confirm
Get-MpPreference | Select-Object -ExpandProperty ExclusionProcess
Get-MpPreference | Select-Object -ExpandProperty ExclusionPath
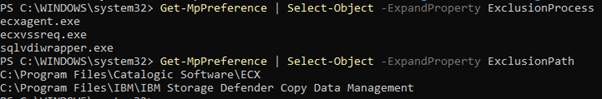
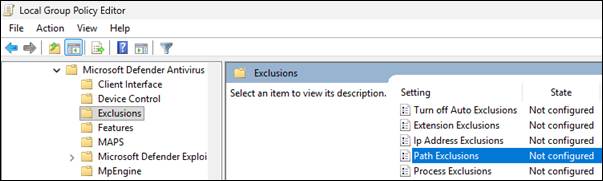
Alternately, via Group Policy (gpedit):
Computer Configuration → Administrative Templates → Windows Components → Microsoft Defender Antivirus → Exclusions
o Process Exclusions: ecxagent.exe, sqlvdiwrapper.exe
o Path Exclusions: full install directory of the CDM agent
2. SQL VDI & VSS Related Path Exclusions
sqlvdiwrapper.exe works through the SQL Server VDI (Virtual Device Interface) and creates shadow copies. Defender often flags the temp/staging areas used during this operation.
# SQL VDI temp and staging paths (adjust volume letters as appropriate)
Add-MpPreference -ExclusionPath "C:\Windows\Temp" # VDI uses temp named pipes here
Add-MpPreference -ExclusionPath "C:\Windows\System32\vss" # VSS writer staging
Add-MpPreference -ExclusionPath "C:\Windows\System32\drivers\etc"
# SQL Server data/log directories (adapt to your SQL instance paths)
Add-MpPreference -ExclusionPath "D:\SQLData" #Path to MDF
Add-MpPreference -ExclusionPath "E:\SQLLogs" #Path to MDF
Add-MpPreference -ExclusionPath "F:\LogBackups" #Path to log *.trn
Important: Microsoft's own SQL Server best-practice guidance recommends excluding SQL data/log/log backup directories from real-time AV scanning. See [Microsoft's SQL Server AV exclusion KB article] (https://learn.microsoft.com/en-us/troubleshoot/sql/database-engine/security/antivirus-and-sql-server).
3. WinRM Session Exclusions — CDM Appliance IP
Microsoft Defender Antivirus (via Windows Defender Firewall + ATP sensor, if enabled) may flag WinRM connections from the CDM appliance because:
- The source IP is an appliance outside the domain trust
- WinRM over HTTP (port 5985) or HTTPS (5986) from a non-domain source triggers lateral movement heuristic.
Recommended mitigations:
a) Add the CDM Appliance to WinRM TrustedHosts
# Replace <CDM_APPLIANCE_IP> with your actual CDM appliance IP or FQDN
Set-Item WSMan:\localhost\Client\TrustedHosts -Value "<CDM_APPLIANCE_IP>" -Force
# Verify
Get-Item WSMan:\localhost\Client\TrustedHosts
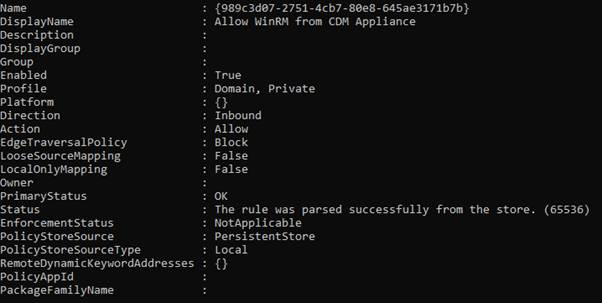
b) Windows Defender Firewall — Allow Inbound WinRM from CDM Appliance only
# Scope WinRM inbound rule to CDM appliance IPs only (replaces "any" source)
New-NetFirewallRule
-DisplayName "Allow WinRM from CDM Appliance"
-Direction Inbound `
-Protocol TCP `
-LocalPort 5985,5986 `
-RemoteAddress "<CDM_APPLIANCE_IP>" `
-Action Allow `
-Profile Domain,Private
# Optionally restrict the existing broad WinRM rule
Set-NetFirewallRule -DisplayName "Windows Remote Management (HTTP-In)" -RemoteAddress "<CDM_APPLIANCE_IP>"
c) If Microsoft Defender for Endpoint (MDE/ATP) is active - Add IOC Exclusion
If you're running the full Microsoft Defender for Endpoint stack (not just the built-in Microsoft Defender AV), the WinRM alerts come from the EDR sensor. You need to suppress those via the MDE portal:
- Microsoft 365 Defender Portal → Settings → Endpoints → Indicators → IP addresses
- Add the CDM appliance IP as an Allow indicator
- Add a suppression rule under Alerts → Suppression Rules scoped to the CDM IP + WinRM process (wsmprovhost.exe)
4. Summary Exclusion Checklist
|
Type
|
Value
|
|
Process
|
ecxagent.exe
|
|
Process
|
sqlvdiwrapper.exe
|
|
Process
|
ecxvssreq.exe
|
|
Path
|
CDM agent install directory
|
|
Path
|
SQL Server data/log/backup directories
|
|
Path
|
C:\Windows\Temp (VDI named pipes)
|
|
WinRM TrustedHosts
|
CDM appliance IP/FQDN
|
|
Firewall Rule
|
Inbound TCP 5985/5986 scoped to CDM appliance IP
|
|
MDE Indicator (if MDE deployed)
|
CDM appliance IP --> Allow + alert suppression on wsmprovhost.exe
|
Verification After Applying Exclusions
# Confirm all exclusions are in effect
Get-MpPreference | Select-Object ExclusionProcess, ExclusionPath, ExclusionIpAddress
# Confirm no active quarantine events for CDM processes
Get-MpThreatDetection | Where-Object { $_.Resources -match "ecxagent|sqlvdi" }
# Check WinRM trusted hosts
winrm get winrm/config/client
After applying these exclusions, trigger a test CDM backup job and monitor Microsoft Defender Antivirus → Protection History to confirm no new alerts are generated for the CDM agent processes or WinRM sessions.